List every legitimate sender
Include mailboxes, forms, newsletters, invoicing and helpdesk tools. Some use separate subdomains. Identify their actual sending domains and required SPF configuration before editing. This avoids unnecessary includes and missing legitimate services.
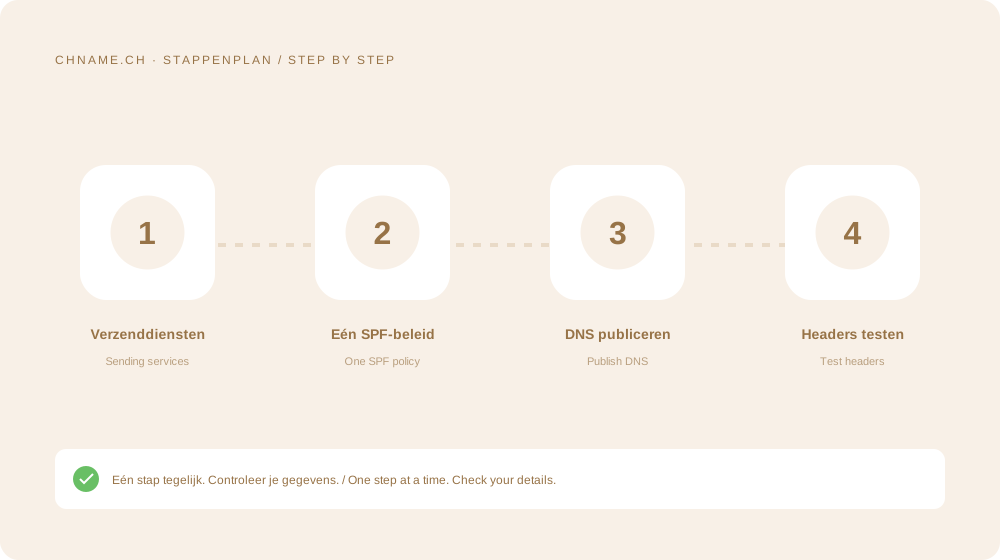
One SPF policy per host
Do not add a separate v=spf1 TXT record for each provider on the same host. Combine required mechanisms into one policy. SPF also limits DNS lookups, so nested includes need review. Test authentication headers on real mail rather than delivery alone.
Your practical checklist
- List sending services.
- Check the active DNS zone.
- Keep one SPF policy per host.
- Test real message authentication.
A useful question
Is SPF sufficient to prevent spoofing?
SPF alone is not a complete solution. Use suitable DKIM and DMARC as well.
Ready to check your name? Start with the exact domain, then compare alternatives. Find a domain →
Sources & further reading
Original guide by chname.ch editorial. Archive dates organise this library; this guide was created and reviewed on . Provider and registry instructions take precedence when requirements change.